Kafka is a powerful engine for event-driven architectures, empowering enterprises to build the custom services they need to get the best out of big data and real-time events. However, when multiple teams, microservices, and compliance requirements converge, Kafka can become complex. Tyk Streams tackles this head-on, providing a unified API management layer to reduce operational overheads and streamline compliance.
Choose Tyk when partners consume over web protocols and you want one API management layer and Developer Portal for REST and event APIs, with in-stream processing. Most partners do not need native Kafka-protocol access, and handing partners direct broker access is a risk Tyk avoids by design: Tyk keeps Kafka private. HTTP, SSE, WebSocket and webhooks let partners integrate without Kafka clients, with API authentication, quotas and connection analytics. Kafka ACLs, broker networking and client-library requirements stay behind that layer.
Publishers connect a portal_webhook output by event_type; partners then select events and register their own webhook URL and HMAC secret in My Apps. Self-service subscriptions keep partner callback registration in the Developer Portal. Optional partner outputs provide destination-specific authentication, transforms and failover in one configuration. Partners sign up to event plans in the Tyk Developer Portal themselves; administrators choose auto-approval or required approval.
AsyncAPI documentation. AsyncAPI is a documentation format, and the Tyk Developer Portal fully supports it: you publish AsyncAPI documentation for your event APIs in the portal, where partners discover them before they request access (see Developer Portal API documentation). The stream configuration itself lives in the API's OpenAPI document as the x-tyk-streaming extension (see API-level configuration).
No stream configuration per partner. One Streams API serves every partner. A single http_server output serves all clients on its path, stream_path and ws_path endpoints (HTTP Server output); broker outputs default to pattern: fan_out, so every output receives every message, and round_robin is opt-in (Broker output). With a portal_webhook output, each partner sets its own webhook URL and HMAC secret in the Developer Portal (webhook subscriptions), and access runs through Portal API Plans with optional auto-approve (API Plans). To give each partner independent offsets, set the Kafka consumer_group per partner from a client attribute such as a JWT claim or API key metadata (Kafka input).
With Tyk Streams, you can simplify async event flows such as Kafka, while applying the same robust security, governance, auditing and other standards across your REST, GraphQL and other APIs. The result? Greater operational efficiency, unified governance, and fewer compliance blind spots and security risks, keeping everyone from your developers to your regulators happy.
Below, we’ll take a look at how Tyk Streams can help you:
- Expose Kafka via web protocols. Avoid the complexity of native Kafka protocol for broad access. Use HTTP, WebSocket, SSE, or GraphQL to make Kafka data accessible to a wider, more innovative audience.
- Centralize security and governance. Tyk Streams folds Kafka event access into the same robust policy engine that governs your REST and GraphQL APIs, ensuring consistent, auditable security.
- Keep Kafka consumer groups in Kafka. Tyk Streams uses standard Kafka consumer groups: set
consumer_groupper stream, statically or from API key metadata, so a shared group load-shares and distinct groups each receive every message, while topic ACLs and broker settings stay in Kafka. - Reduce overhead and boost compliance. Replace custom bridging microservices with Tyk’s out-of-the-box bridging. Simplify auditing and compliance with persistent logs, a single policy store, and uniform enforcement across APIs.
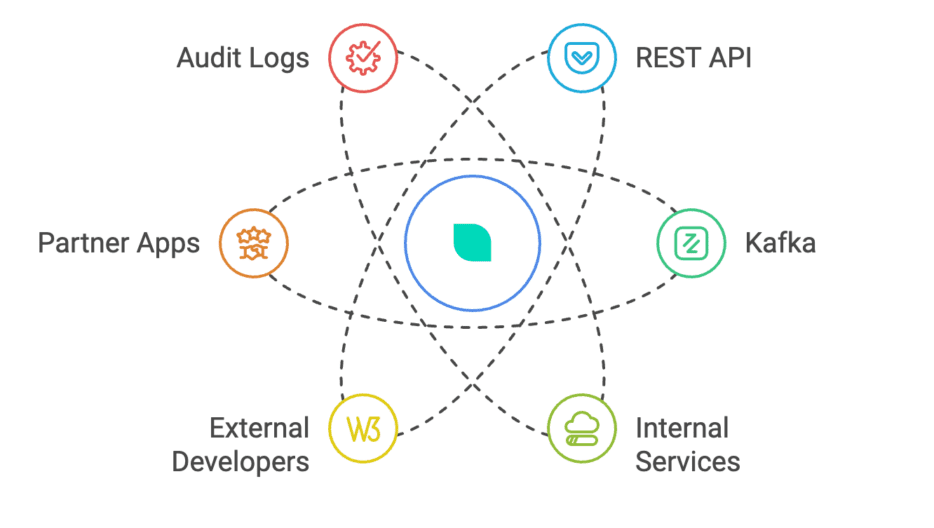
Five challenges of governing Kafka
While Kafka provides its own ACLs (Access Control Lists), consumer groups, and security features, managing them directly can be time-consuming—especially if you need to securely expose these Kafka events to broader audiences or integrate with standard web tooling. Common challenges in governing Kafka natively include:
1. Complex ACL management
Kafka’s ACLs are robust but require careful configuration for each topic, user, or group. Keeping them synchronized across multiple brokers or environments is prone to human error.
2. Consumer group coordination
As usage expands, teams spin up additional consumer groups. Tracking how they authenticate, read offsets, and manage partitions can become unwieldy.
3. Siloed security tools
Many organizations rely on best-of-breed web security solutions—like WAFs or SSO providers—that don’t integrate easily with native Kafka protocols. This means you often have to manage separate rule sets for Kafka and for your REST APIs.
4. Lack of unified governance
Large enterprises want consistent authentication, authorization, and auditing across all API types—both synchronous and asynchronous. Kafka’s native security stands apart from your typical REST or GraphQL layers, increasing complexity.
5. Compliance blind spots
Regulated industries need comprehensive logs of who accessed which data, through which method, and when. Kafka’s logs capture broker-level activity but reconciling them with broader organizational compliance can be cumbersome.
Tyk Streams: One point of control
Tyk Streams brings the benefits of API management to Kafka events, without exposing the native Kafka protocol. By translating Kafka data into familiar web protocols (HTTP, WS, SSE, GraphQL), Tyk Streams centralizes your security and compliance policies in one place. And because it doesn’t provide direct access to the native Kafka protocol, you can leverage well-understood web security tools (e.g., WAFs, DLP, TLS termination) without diving into low-level broker configurations.
This delivers a range of benefits that contribute to easier event management and governance, along with enhanced security.
No more native Kafka protocol headaches
Standard web endpoints
Tyk Streams publishes Kafka events as endpoints that speak HTTP/WebSocket/SSE/GraphQL. This approach unlocks a world of existing tools—like web application firewalls (WAFs)—and simplifies how teams access real-time data.
Familiar tooling
With Tyk Streams, you can employ typical API management strategies: API keys, OAuth2 flows, JWT tokens, rate limiting, and more. You don’t need specialized Kafka protocol expertise on the client side.
Centralizing security policies
Unified access control
Instead of creating new ACL entries in Kafka for every user or topic, you can define one access policy in the Tyk Dashboard. When a client requests data, Tyk Streams checks against Tyk’s policy engine—covering both synchronous and asynchronous APIs.
Flexible consumer group strategy
Tyk Streams joins the standard Kafka consumer group named in its Kafka input (consumer_group), with the same delivery semantics as any Kafka consumer, while topic ACLs and broker policies stay in Kafka. Tyk Streams can then dynamically map client attributes to these groups. For example:
- Use a JWT claim (like a tenant ID) to route data to the correct consumer group.
- Rely on a static consumer group assignment, if you prefer more rigid isolation.
- Incorporate any client metadata to determine which consumer group or partition they should connect to.
Tyk Streams consumes from and publishes to Kafka, and combines multiple inputs and outputs in one stream. Receive an event, enrich it through http inside a branch processor, filter or transform it with mapping/Bloblang, and deliver to Kafka, webhooks, SSE or WebSocket. See the processing examples. Streams APIs are defined in a standard OpenAPI document via the Tyk OAS x-tyk-streaming extension; see API-level configuration.
The consumer group and per-consumer stream settings can reference API key metadata ($tyk_meta.KEY_NAME) and Tyk context variables ($tyk_context.remote_addr): administrators group consumers per developer, per organisation or by client IP and filter fields, event types and sources by policy in one YAML configuration. Shared Kafka consumer_group values load-share; distinct groups receive every message. Kafka input checkpoint settings preserve at-least-once delivery; web-output acknowledgement behaviour is documented separately.
How partners consume Kafka through Tyk. Tyk deliberately keeps your native Kafka listener private: partners never receive broker addresses, Kafka ACL entries or client-library requirements, and consume over webhooks, SSE, HTTP streaming or WebSocket with API keys or OAuth and per-plan quotas. Partners that run Kafka themselves keep their own Kafka clients: the kafka output publishes filtered, transformed events into a partner-owned cluster or topic with that partner's credentials. On your side, each stream joins a standard Kafka consumer_group: a shared group load-shares, distinct groups each receive every message, and Kafka checkpointing preserves at-least-once consumption.
One Kafka input, every partner entry point. The same stream can deliver to webhooks (portal_webhook or the http_client output), serve WebSocket and continuous HTTP streaming consumers from the http_server output (ws_path, stream_path), mediate to SSE, and publish back to Kafka.
Operational overhead drops
Eliminate custom bridging
Without Tyk Streams, teams often build microservices to translate Kafka data into HTTP-friendly formats or to handle security logic. Tyk Streams removes the need for extra microservices—configuration in Tyk handles the bridging under the hood.
Rely on standard dev & ops practices
By exposing Kafka events as web protocols, you can plug into existing CI/CD pipelines, alerting systems, and monitoring tools—just like any other API.
Enhanced compliance and governance
Unified auditing
Tyk 5.7 introduced persistent audit logging, so you can track who requested which Kafka events, via which endpoint, and when. Centralizing all this in Tyk’s audit logs streamlines compliance across microservices and event-driven components.
Consistent policies for all APIs
With Tyk Streams, your REST, GraphQL, and event APIs share the same security model. Compliance officers see a single policy framework, making it easier to demonstrate consistency with regulations like GDPR or PCI DSS.
Visibility and control
Tyk Streams also integrates with Tyk’s analytics and telemetry features, so you can observe how often certain Kafka events are accessed, by whom, and from which locations. This granular visibility can help identify suspicious behavior or optimize capacity planning.
Real-world scenario: Securely exposing payment events
Consider a fintech startup that processes high volumes of transactions in Kafka. It needs to expose certain payment updates to internal data analysts and external partners—without granting direct broker access.
Kafka setup
- Topics like transactions_completed, transactions_failed exist in Kafka.
- Consumer groups define who can read from each topic.
Tyk Streams configuration
- The startup configures Tyk Streams to expose these topics over HTTP or SSE endpoints.
- Policies in Tyk require OAuth2 tokens, ensuring each user is authenticated before streaming any data.
Client consumption
- Internal data analysts query real-time payment updates through an SSE endpoint in their web dashboards, using their corporate SSO credentials.
- External partners integrate via a secure HTTP-based webhook URL, receiving events only related to their transactions.
Outcome
- No custom bridging microservices or specialized Kafka protocol knowledge required.
- Auditors can see all event subscriptions and deliveries in Tyk’s centralized logs.
- The startup ensures that external partners never directly touch the Kafka broker or require specialized ACL entries—Tyk Streams handles it all.
Getting started with Tyk Streams and Kafka
Upgrade to Tyk 5.7
- Make sure you’re on the latest version to unlock Tyk’s event-native API management.
Enable Tyk Streams
- Tyk Streams requires the Enterprise Edition Gateway image (
tykio/tyk-gateway-ee) and a Dashboard license that includes thestreamsclaim; on Tyk Cloud, contact support to enable it. Then, in your Tyk Dashboard, navigate to “Streams” and configure a new stream pointing to your Kafka cluster. - Define which topics are exposed and how Tyk Streams should interact with existing consumer groups.
- Choose your output protocol: HTTP, WS, SSE, or GraphQL.
Configure security policies
- Create or update a policy in Tyk that sets authentication (API keys, JWT, OAuth2) and any rate limits or quotas.
- Map your existing Kafka consumer group logic to Tyk’s policy engine to ensure the right data flows to the right place.
Publish and monitor
- Test your new endpoints, ensuring data is streaming correctly.
- Publish your event-driven APIs to Tyk’s developer portal for self-service discovery—internally or externally.
- Monitor consumption and view audit logs for compliance or debugging.
Conclusion
Securing and managing Kafka at scale doesn’t have to be a juggling act of ACLs, custom microservices, and siloed security tools. Tyk Streams provides a unified API management layer that exposes Kafka events over standard web protocols—letting you tap into existing security infrastructure, reduce operational complexity, and meet compliance requirements head-on.
Ready to unify Kafka governance under Tyk Streams?
- Explore the Tyk Streams docs for configuration details.
- Dive into our Kafka input documentation for best practices on topics and consumer groups.
- Visit our developer portalto see how Tyk can help secure and simplify your broader API ecosystem.
Empower your teams, safeguard your data, and streamline your event-driven architecture—starting now with Tyk Streams.