

Introduction
Tyk Gateway can discover upstream addresses at runtime, instead of using a fixed target list. When you add, remove or replace upstream instances, Tyk Gateway sends traffic to the new set of addresses. You don’t need to change or reload the API. Tyk Gateway offers two ways to discover upstream addresses:
An API can use only one of these methods at a time.
If you use a service mesh, the mesh can do service discovery instead; see Service Mesh Discovery.
Registry-Based Service Discovery
With registry-based service discovery, Tyk Gateway queries a third-party service registry, such as Consul, etcd or Eureka, to find the upstream addresses for an API. It reads the addresses from the JSON response of the registry. You can use them as a single upstream URL or as the load balancing target list. We recommend using registry-based service discovery together with circuit breakers. A circuit breaker quickly detects an upstream that has failed, and service discovery then supplies the replacement addresses.How Service Discovery Works
Tyk Gateway calls the query endpoint of the registry and extracts each upstream address from the response. It caches the result and queries the registry again when the cache expires or if a request to the upstream times out. If the query fails, Tyk Gateway sends requests to the upstream URL configured in the API definition. If the registry returns an empty list, Tyk Gateway keeps using the last list that it received.Configure in Tyk Dashboard
In the API designer, open the Upstream section of your API and enable Service discovery. Select a preset for your registry to fill in the response settings automatically, or select Custom. Then enter the Service query endpoint. Use Advanced settings to change how Tyk Gateway reads the response from the registry.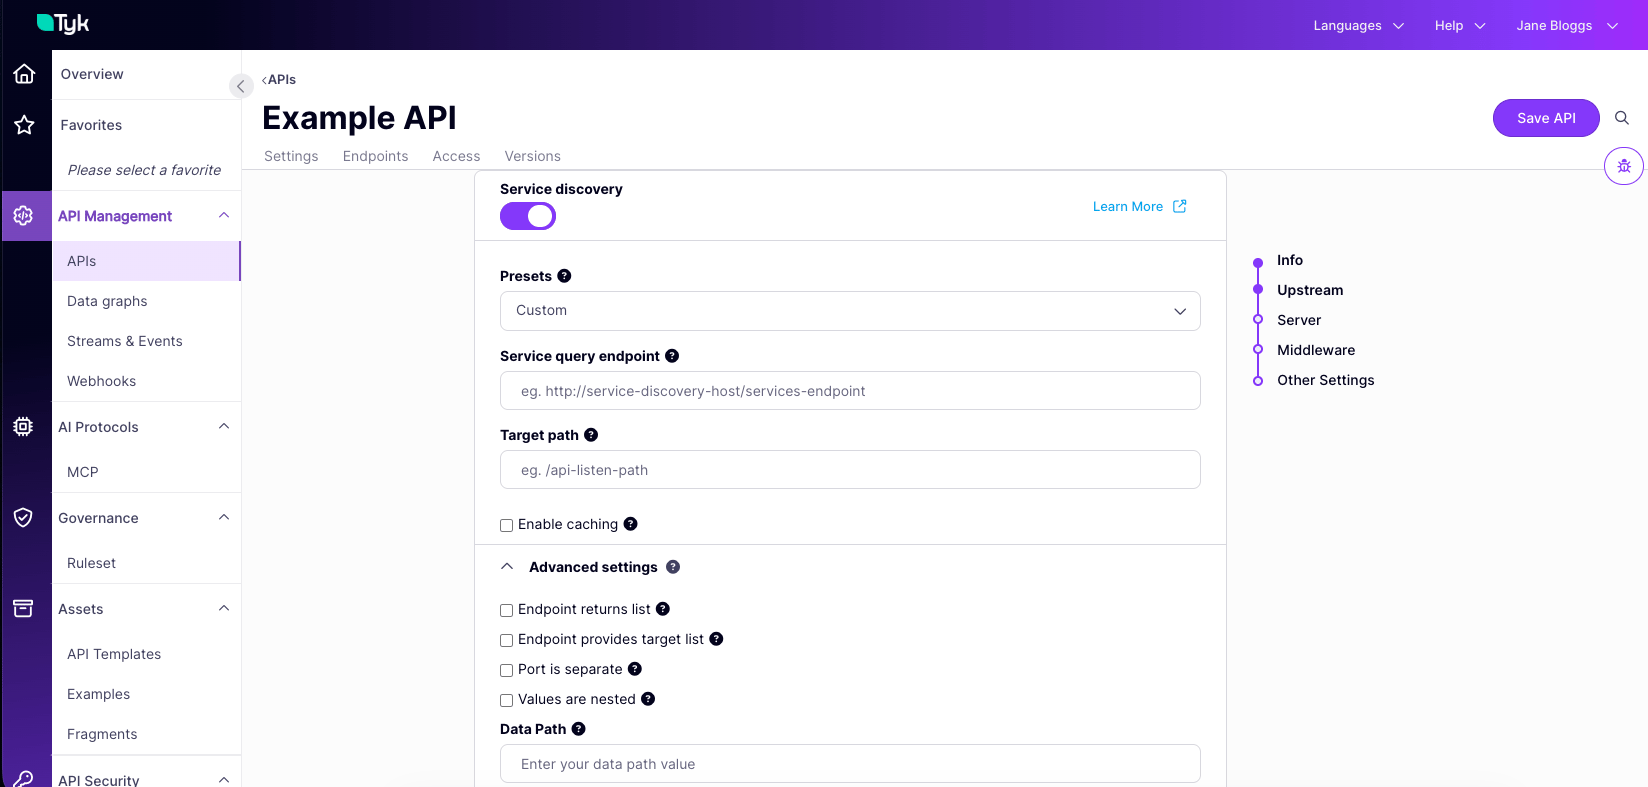
Configure in the API Definition
Configure service discovery in theupstream.serviceDiscovery section of the Tyk Vendor Extension:
If
cache.enabled is false, or cache.timeout is 0, Tyk Gateway caches the addresses for the default time in its configuration. Set this with service_discovery.default_cache_timeout. The default is 120 seconds.proxy.service_discovery. See the Tyk Classic API definition reference for full details of the field names.
Examples
These examples show theserviceDiscovery settings for some common registries. Add enabled: true and your queryEndpoint to each example.
- Consul
- etcd
- Eureka
- Mesosphere
- ZooKeeper
The Consul catalog API returns an array of service instances:
DNS Discovery
Available from Tyk 5.16.0
When to Use DNS Discovery
gRPC uses HTTP/2, which carries many requests over one long-lived connection. If the upstream is a Kubernetes Service, Tyk Gateway opens this connection to one pod and sends every request over it. The other pods receive no traffic, and new pods from autoscaling stay idle. DNS discovery solves this. Tyk Gateway resolves the upstream hostname at a regular interval and uses every address as a load balancing target. It picks up added and removed pods at the next lookup, so you don’t need to reload the API. DNS discovery works with any cleartext HTTP/2 (h2c://) upstream, such as a gRPC service.
Requirements
To use DNS discovery:- Use the
h2c://scheme and a hostname in the upstream URL. - Enable load balancing.
- Disable registry-based service discovery.
- Make sure that the hostname resolves to the address of each upstream instance.
https://), IP addresses or localhost. It supplies the target list, and the load balancer distributes requests across it.
In Kubernetes, use a headless Service (clusterIP: None). A standard Service resolves to a single cluster IP, so every request still reaches the same pod.
Configuration
Configure DNS discovery in theupstream.dnsDiscovery section of the Tyk Vendor Extension:
Durations use a human-readable format, such as
30s or 2m.
If using Tyk Classic, configure the equivalent settings in proxy.dns_discovery. See the Tyk Classic API definition reference for full details of the field names.
The Tyk Dashboard API designer doesn’t have fields for DNS discovery. To configure it, select Actions > View API definition and edit the API definition directly.
How DNS Discovery Works
Request Distribution: at each lookup, Tyk Gateway builds the target list from the addresses that DNS returns. The load balancer then rotates requests across these addresses. APIs that use the same hostname share one lookup. Host Header: Tyk Gateway connects to each discovered address. It sends the hostname from the upstream URL as the Host (HTTP/2:authority) of each request. The upstream receives the service name in every request.
No Addresses Available: until the first lookup succeeds, requests fail with 503 Service Unavailable and the message all hosts are down. The same happens when DNS returns no addresses twice in a row, for example when a Kubernetes Service has no ready pods. Tyk Gateway ignores a single empty answer, so a short gap doesn’t stop traffic. It never falls back to the upstream URL.
DNS Resolver Unavailable: if DNS lookups fail, Tyk Gateway keeps using the last known addresses. When staleTTL expires, requests fail with 503 until a lookup succeeds. Each API uses the staleTTL value in its API definition, even when APIs share a hostname.
Removed Addresses: when DNS no longer returns an address, Tyk Gateway sends no new requests to it after the next lookup. Open connections to the address, such as long-lived gRPC streams, stay open until they become idle. If you enable connection draining, they close when the drain timeout expires.
Troubleshooting
Tyk Gateway logs every DNS discovery event with the prefix[DNS DISCOVERY]. Search the Tyk Gateway log for this prefix to see what happens to an API.
Check That DNS Discovery Is Active
When Tyk Gateway loads an API that uses DNS discovery, it logs this message at info level:
host, refresh_interval, stale_ttl and drain_timeout that Tyk Gateway uses.
Common Problems
Service Mesh Discovery
If you use a service mesh, the mesh can do service discovery instead of Tyk Gateway. Tyk Gateway sends requests to the mesh, and the mesh routes each request to the correct service instance. You don’t need to enable service discovery or DNS discovery in the API definition.Linkerd
This example is a Tyk community contribution. It uses the router configuration of Linkerd 1.x. Linkerd 2.x doesn’t use this configuration.
Host header. Tyk Gateway sets the Host header to the upstream host, so Linkerd must use a different header. Add this configuration to the linkerd.yaml file in the config/ directory of Linkerd:
Custom-Header to every request, with the Linkerd app-id of the service as its value: