

Availability
Tyk AI Studio supports Single Sign-On (SSO) integration, allowing users to authenticate using their existing credentials from external Identity Providers (IdPs). This simplifies login, enhances security, and centralizes user management.
SSO is for users who sign in to AI Studio. For machine clients that send requests to an Edge Gateway, use the OAuth2 Client Credentials plugin.
Purpose
The SSO integration aims to:- Allow users to log in to Tyk AI Studio using their familiar corporate or social identity credentials.
- Eliminate the need for separate Tyk AI Studio-specific passwords.
- Improve security by leveraging the organization’s existing IdP infrastructure and policies (e.g., MFA).
- Streamline user provisioning and de-provisioning (depending on IdP capabilities and configuration).
Technology: Tyk Identity Broker (TIB)
Tyk AI Studio leverages the embedded Tyk Identity Broker (TIB) component to handle SSO integrations. TIB acts as a bridge between Tyk AI Studio (the Service Provider or SP) and various external Identity Providers (IdPs).Supported Protocols & Providers
TIB enables Tyk AI Studio to integrate with IdPs supporting standard protocols, including:- OpenID Connect (OIDC): Commonly used by providers like Google, Microsoft Entra ID (Azure AD), Okta, Auth0.
- SAML 2.0: Widely used in enterprise environments (e.g., Okta, Ping Identity, ADFS).
- LDAP: For integration with traditional directory services like Active Directory.
- Social Logins: Providers like GitHub, GitLab, etc. (often via OIDC).
Prerequisites
- A callback URL to register with your IdP. Every profile gets a callback URL in the form
https://<your-ai-studio-domain>/auth/<profile-id>/<provider>/callback. AI Studio only assigns the<profile-id>once you create the profile. Create the profile with placeholder values first. Then note its ID from the profile list, register the callback URL with your IdP, and finish the profile configuration. - For OIDC: Client ID, Client Secret, and either an Issuer URL or a Discovery Endpoint from your IdP.
- For SAML: your IdP’s SSO URL, IdP Issuer or Entity ID, and the IdP’s public certificate. Your IdP will also ask for the SP Entity ID, which is Tyk AI Studio’s own identifier.
- Certificate format for SAML (current limitation). AI Studio’s certificate manager is file system based. Save the certificate as a file that the AI Studio server process can read. Point the profile configuration to that file’s path. There is currently no way to upload a certificate through the UI.
Configuration (Admin)
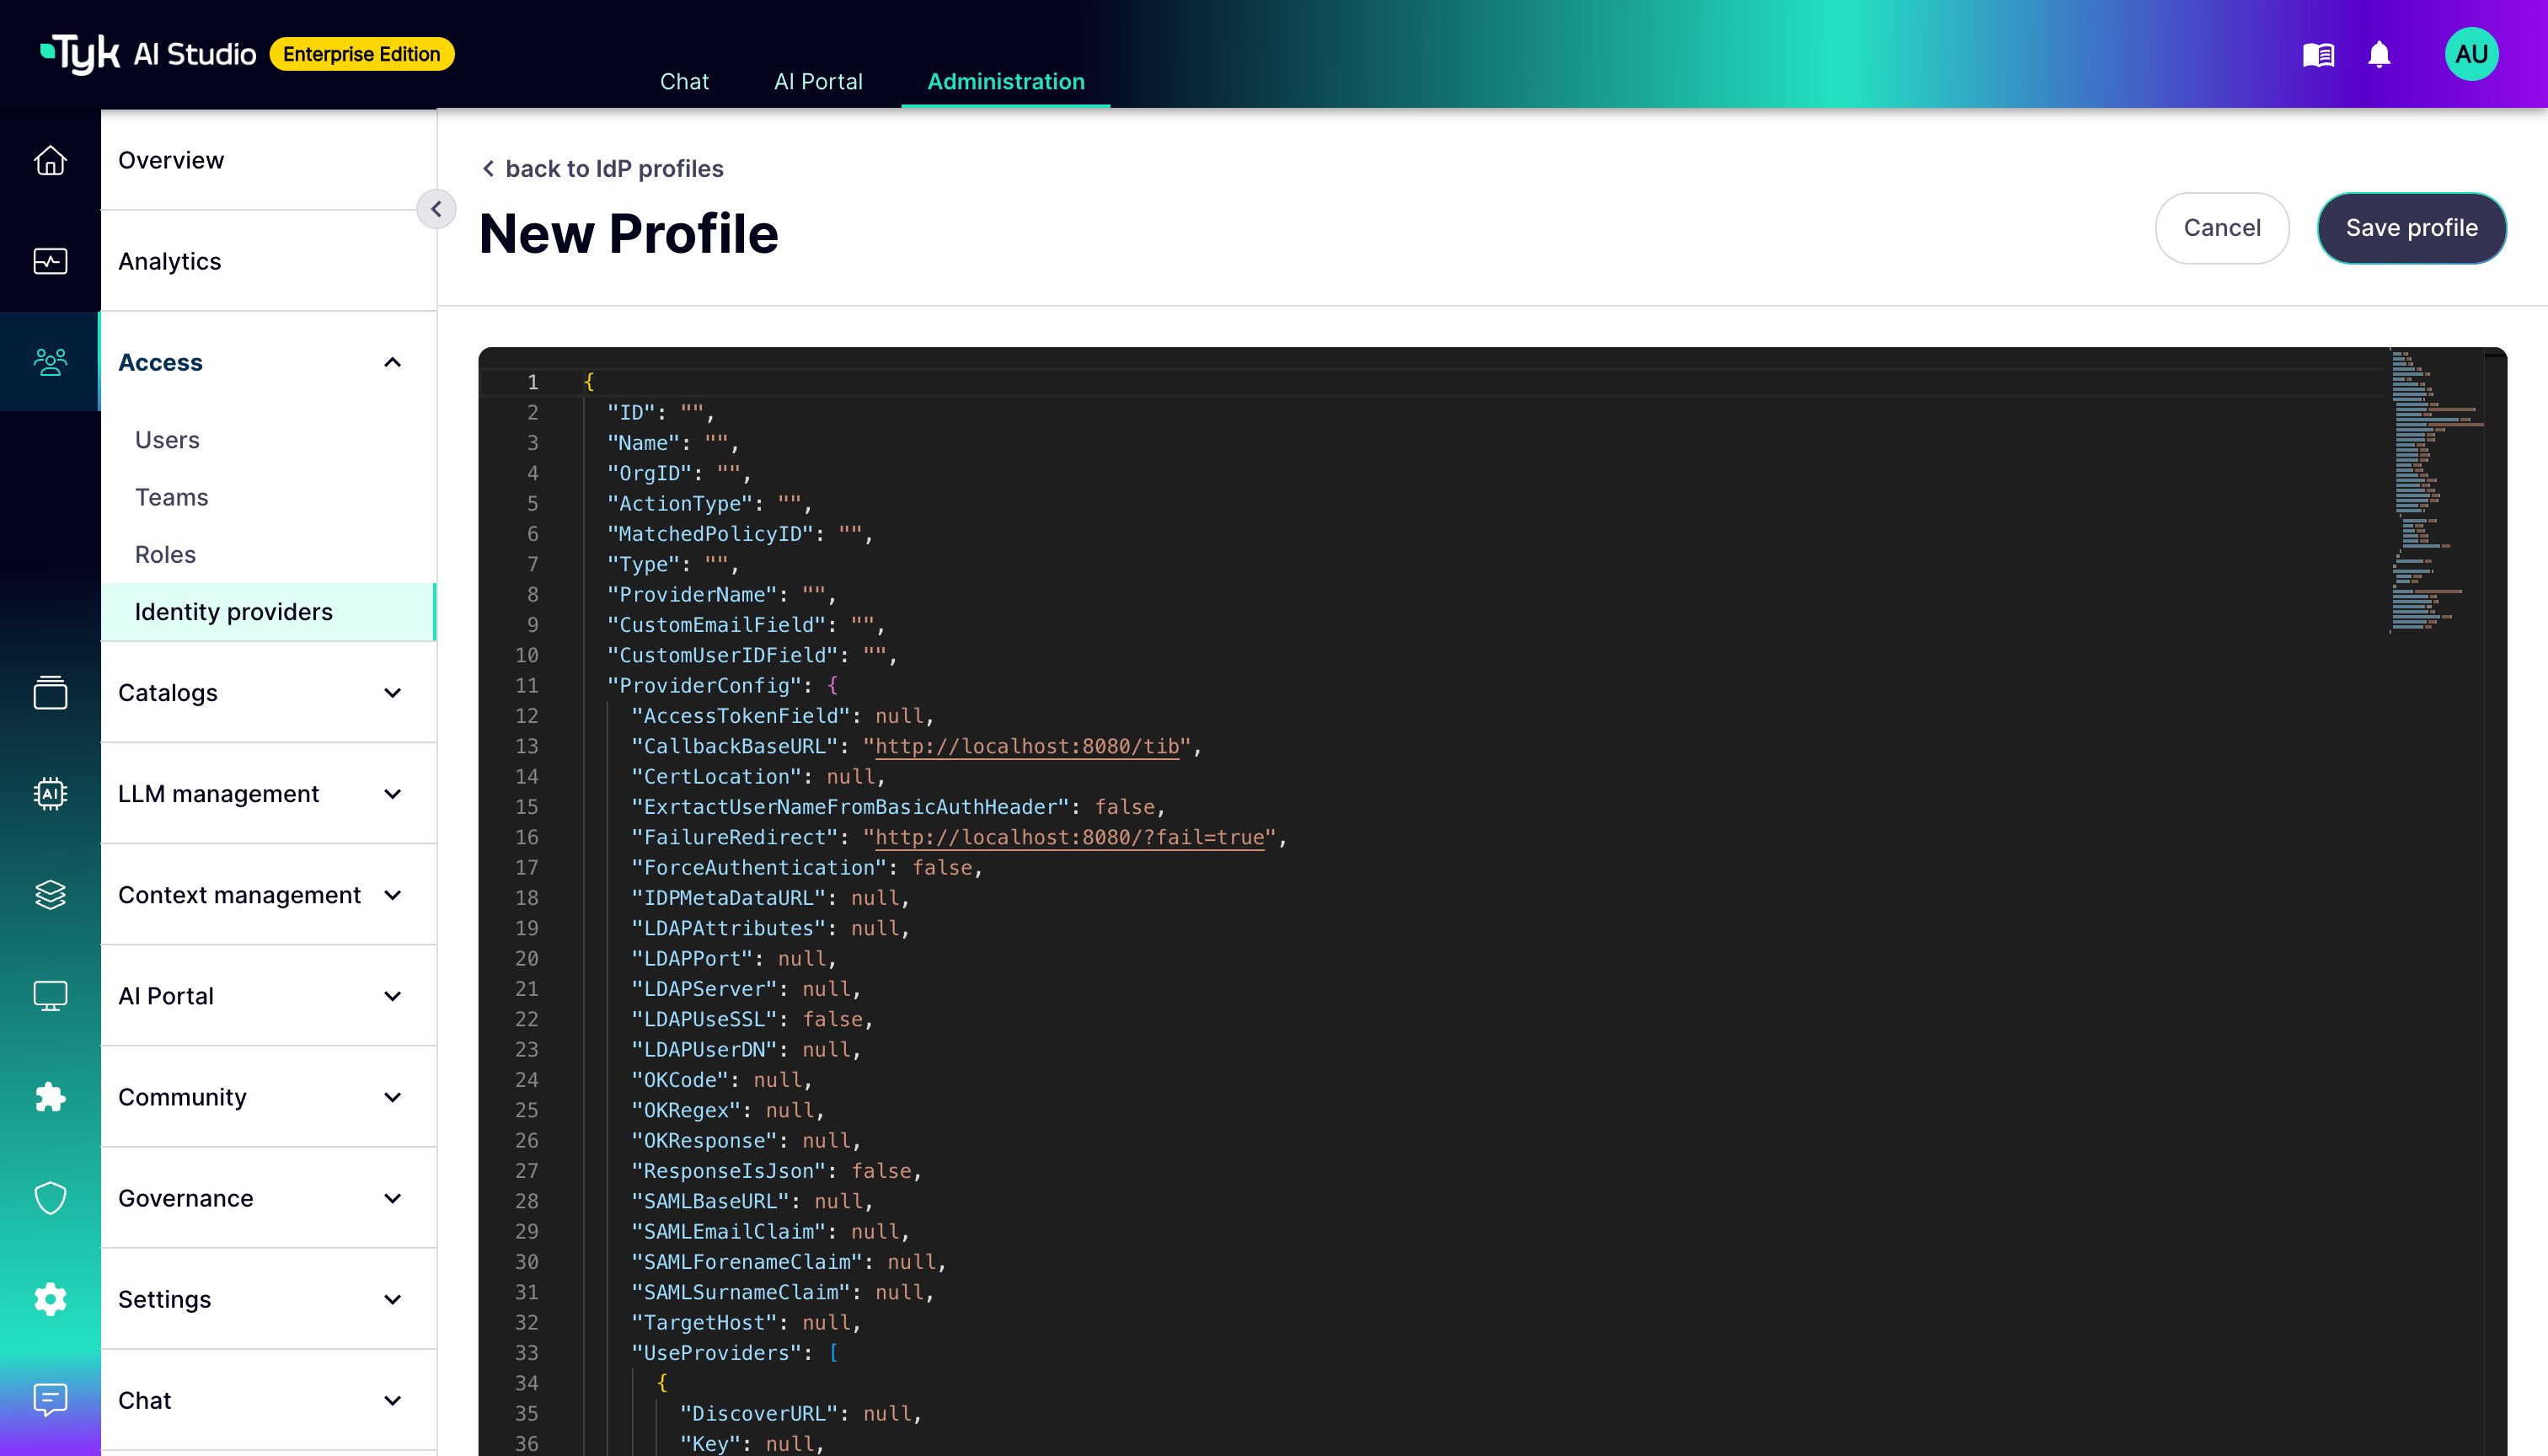
Administrators configure SSO providers within the Tyk AI Studio administration interface (likely via TIB’s configuration settings exposed through Tyk AI Studio):- Select Protocol: Choose the appropriate protocol (OIDC, SAML, etc.).
-
Provider Details: Enter the specific configuration details required by the chosen protocol and IdP.
- OIDC Example: Client ID, Client Secret, Issuer URL, Discovery Endpoint.
- SAML Example: IdP SSO URL, IdP Issuer/Entity ID, IdP Public Certificate, SP Entity ID (Tyk AI Studio’s identifier).
-
Profile Mapping: Configure how attributes received from the IdP (e.g., email, name, group memberships) map to Tyk AI Studio user profiles.
- Identify which IdP attribute contains the unique user identifier (e.g.,
email,sub,preferred_username). - Map IdP attributes to Tyk AI Studio user fields (e.g.,
given_name-> First Name,family_name-> Last Name).
- Identify which IdP attribute contains the unique user identifier (e.g.,
-
Group Mapping (Optional but Recommended): Configure rules to automatically assign users to Tyk AI Studio Groups based on group information received from the IdP.
- Example: If the IdP sends a
groupsclaim containing “Tyk AI Studio Admins”, map this to automatically add the user to the “Administrators” group in Tyk AI Studio. - AI Studio reads the Team membership from the claims at every login, so the IdP stays the source of truth. In the Enterprise Edition, you can assign roles to Teams. An IdP group can then give access to the admin console.
- Example: If the IdP sends a
-
New User Defaults: Select the interfaces for new users from this profile. The options are New users see the AI Portal (
new_user_show_portal) and New users see Chat (new_user_show_chat). Both are on by default. AI Studio applies them only when it creates the user. Existing users keep the values that an administrator set. -
Enable Provider: Activate the configured IdP for user login.
Login Flow
When SSO is enabled:- User navigates to the Tyk AI Studio login page.
- User clicks a button like “Login with [Your IdP Name]” (e.g., “Login with Google”, “Login with Okta”).
- User is redirected to the external IdP’s login page.
- User authenticates with the IdP (using their corporate password, MFA, etc.).
- Upon successful authentication, the IdP redirects the user back to Tyk AI Studio (via TIB) with an authentication assertion (e.g., OIDC ID token, SAML response).
- TIB validates the assertion and extracts user profile information.
- Tyk AI Studio finds an existing user matching the unique identifier or provisions a new user account based on the received profile information (Just-In-Time Provisioning). A new user gets the New User Defaults of the profile.
- Team memberships are updated based on configured mapping rules.
- The user is logged into Tyk AI Studio.
Provisioned Users, API Keys, and Offboarding
- Origin: AI Studio records a user from SSO with the origin SSO. It also records the profile that created the user. The Users list shows the origin, and you can filter on it. A user who registered before you turned on SSO keeps their original origin.
- No password and no API key: AI Studio creates SSO users without a local password and without an API key. Administrators cannot issue a key to an SSO user unless you set
ALLOW_SSO_USER_API_KEYS=true. If you do not set it, the console does not show the option. - Key liveness: When keys are allowed, the key of an SSO user has a liveness period,
SSO_API_KEY_LIVENESS. The key works only if the user logged in through the identity provider during this period. The default is720h(30 days). When you remove a user at the IdP, the user loses API access automatically at the end of the period. Set a shorter period if your offboarding policy requires faster removal of access. Set it to0to turn off the check. If you turn off the check, the key of a user that you remove at the IdP continues to work until you disable the user or revoke the key in AI Studio. - Offboarding: When you remove or disable a user at the IdP, new SSO logins stop.
Benefits
- Improved User Experience: One less password to remember.
- Enhanced Security: Leverages established IdP security policies.
- Centralized Control: User access can often be managed centrally via the IdP.
- Simplified Onboarding/Offboarding: AI Studio creates users at their first login. The API access of SSO users depends on recent IdP logins. For the manual steps, refer to Provisioned Users, API Keys, and Offboarding.